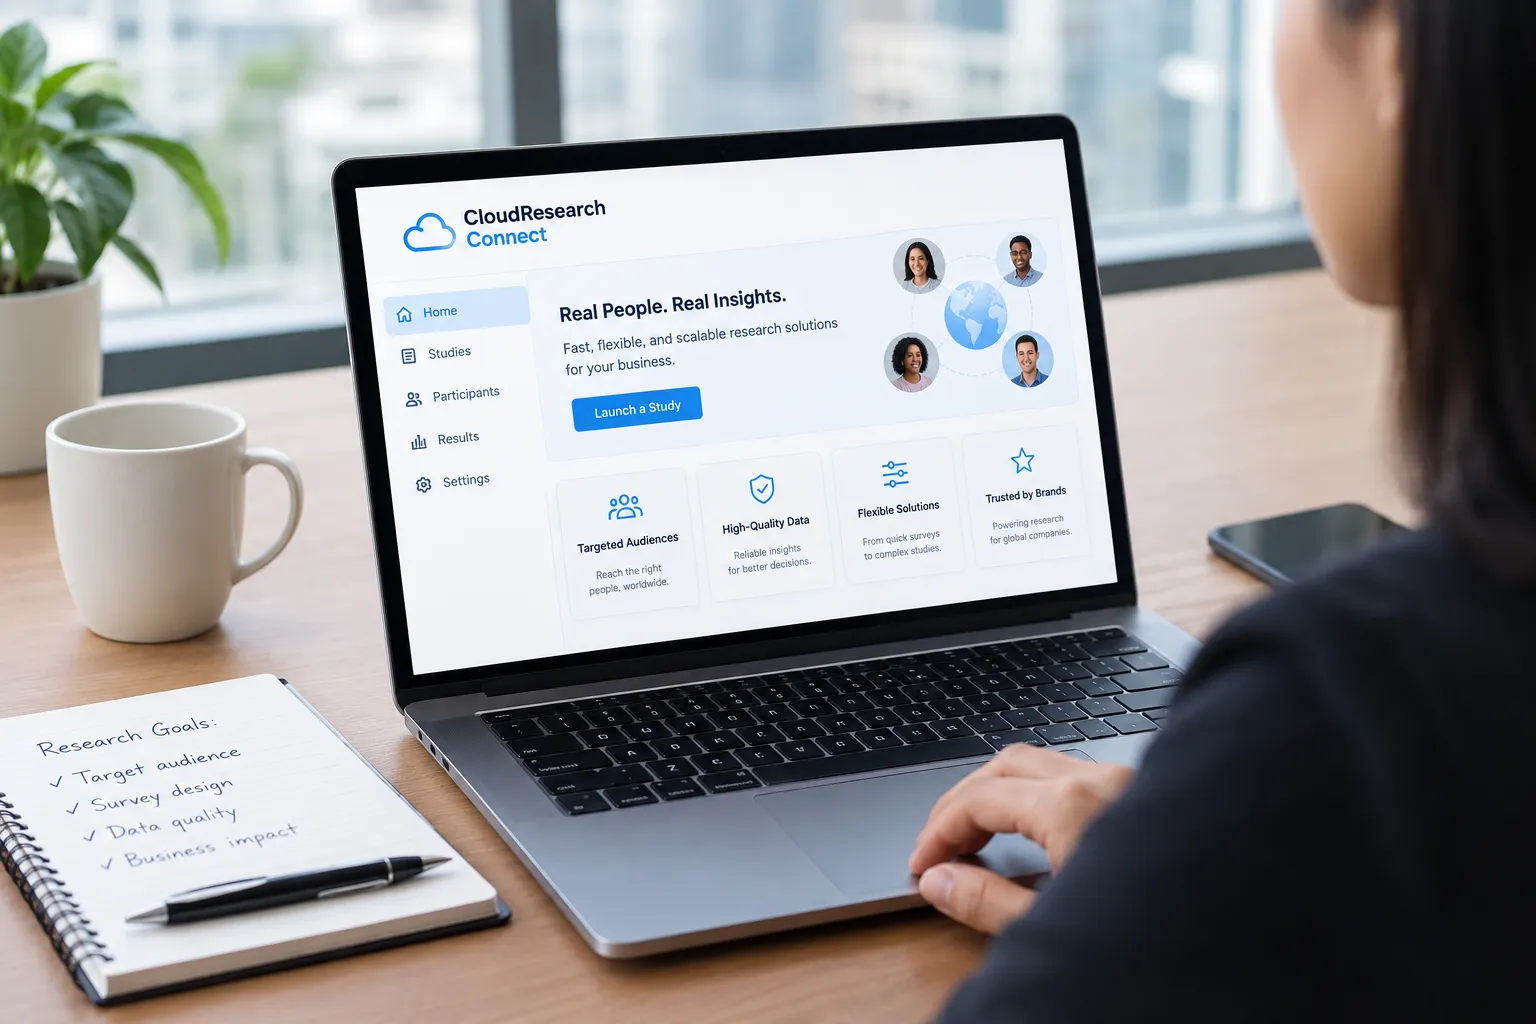
Manufacturers increasingly connect operational technology (OT) with information technology (IT).
That connectivity enables valuable capabilities.
Production data can inform business decisions. Maintenance teams can monitor equipment remotely. Enterprise systems can provide better visibility into inventory, scheduling, and output.
But connectivity also creates dependencies that need to be managed.
A cybersecurity incident affecting enterprise systems can disrupt manufacturing operations even when attackers don’t directly compromise industrial control equipment.
For a manufacturer, that can mean lost production, missed customer commitments, recovery expenses, and operational disruption.
A manufacturing cybersecurity incident isn’t just an IT problem. It can become a business continuity problem.
What is IT/OT convergence?
IT/OT convergence is the integration of enterprise information systems with the technologies that monitor and control industrial operations.
IT typically supports business applications, communications, data management, and enterprise infrastructure.
OT supports physical processes, industrial equipment, and production control.
Connecting these environments can improve operational visibility and decision-making.
It also requires coordination between teams that may have different priorities, technical requirements, and risk tolerances.
What does the latest industrial cybersecurity research show?
The Dragos 2026 OT/ICS Cybersecurity Report, covering 2025 activity, describes ransomware and other threats affecting industrial organizations.
The report identifies manufacturing as a major target and highlights the importance of visibility, detection, and response capabilities.
The submitted research also references a 42-day average ransomware dwell time in OT environments and a substantially shorter response period among organizations with more complete OT visibility.
Those comparisons should be checked against the original report’s definitions and methodology before publication.
The broader lesson is clear.
Manufacturers need to understand which systems are connected, what those systems depend on, and how a disruption could affect production.
How should manufacturers manage IT/OT cybersecurity risk?
A practical approach includes:
- Establish visibility. Maintain an inventory of connected industrial systems, devices, and important dependencies.
- Assign shared accountability. Clarify responsibilities across IT, OT, operations, and security leadership.
- Segment networks appropriately. Limit unnecessary connections between enterprise and industrial environments.
- Control access. Review vendor connections, privileged accounts, remote access, and authentication.
- Prepare for disruption. Establish and test recovery procedures that reflect production requirements.
- Include security early. Evaluate cybersecurity requirements during project planning rather than after deployment.
Security controls should reflect the operating requirements of industrial environments.
Manufacturing systems often have availability and safety considerations that differ from conventional enterprise IT.
The objective isn’t to eliminate connectivity.
It’s to support useful connectivity without creating unmanaged operational risk.