Not every acquired company introduces the same security challenges.
The most important risks depend on the nature of the business, its technology environment, the information it handles, and how it will operate within the platform.
However, several areas deserve particular attention.
1. Inconsistent Security Standards Across Acquired Businesses
One company may require multifactor authentication for critical systems. Another may use it inconsistently. A third may have limited visibility into who has access to sensitive information.
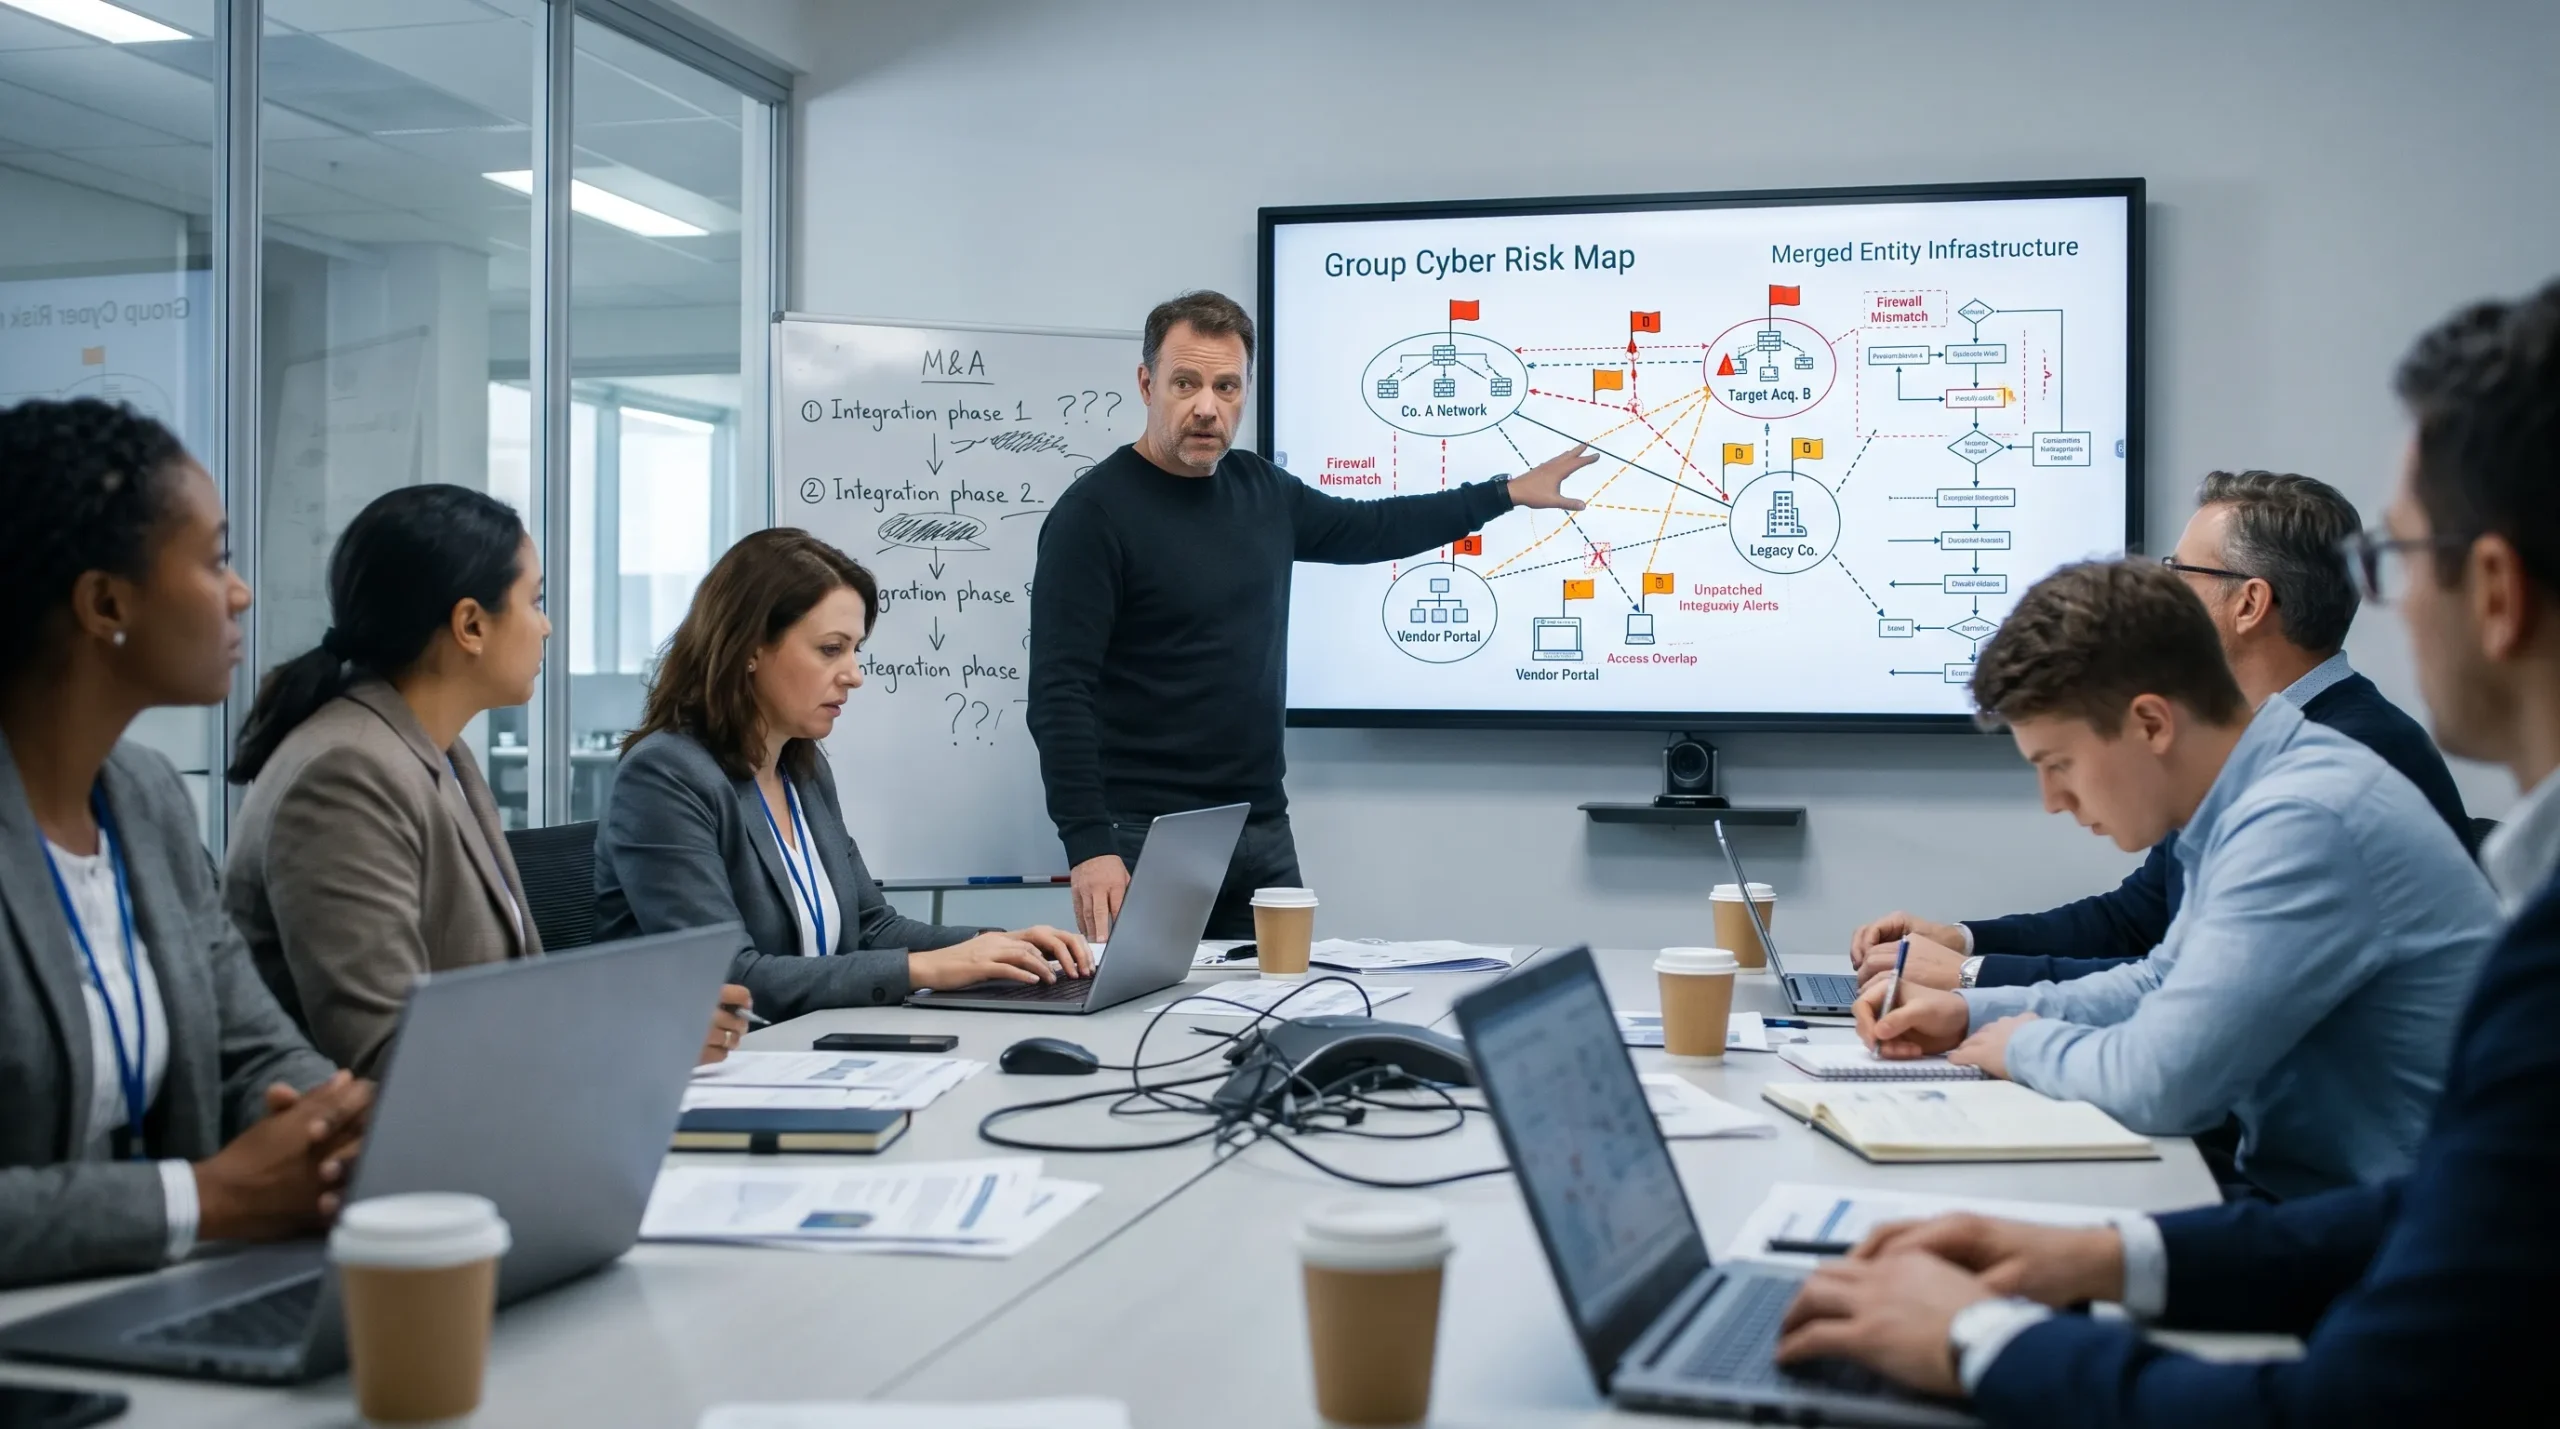
Backup procedures, software updates, vendor oversight, and incident response practices may also differ.
Each business may believe its existing approach is sufficient.
But inconsistent controls make it harder for platform leadership to understand the organization’s overall exposure.
The concern becomes greater when systems and data are shared across businesses.
What leadership should ask: Do we have minimum cybersecurity requirements that apply across the platform, regardless of which business was acquired?
Without a common baseline, security decisions can remain fragmented even as operations become more integrated.
2. Aging Technology and Unresolved Vulnerabilities
Acquired businesses may rely on older applications, unsupported software, or infrastructure that hasn’t received consistent maintenance.
These systems may remain essential to daily operations.
Replacing them immediately may not be practical, particularly when the acquisition strategy includes other operational priorities.
But leaving known vulnerabilities unaddressed can create exposure that grows more difficult to manage over time.
What leadership should ask: Which business-critical systems present the greatest security risk, and what is the plan for addressing them?
The goal isn’t to modernize every system at once.
It’s to understand which vulnerabilities could materially affect business operations and prioritize accordingly.
3. Limited Visibility Into Third-Party Risk
Every acquired business brings vendor relationships.
Those vendors may provide cloud hosting, financial applications, customer management platforms, outsourced IT support, or other essential services.
Some may have access to sensitive information or critical systems.
As acquisitions accumulate, the platform can inherit a growing network of third-party dependencies without a consolidated understanding of the risks involved.
What leadership should ask: Do we know which vendors have access to critical systems and sensitive information across our acquired businesses?
Understanding these relationships is an important part of evaluating platform-wide cybersecurity exposure.
4. Unclear Ownership of Cybersecurity Decisions
Cybersecurity responsibilities are often distributed across IT teams, business unit leaders, external providers, and executive leadership.
That structure can work when responsibilities are clearly defined.
But acquisitions can introduce overlapping roles and gaps in accountability.
One business may rely on an outsourced IT provider. Another may have an internal security team. A third may depend on a general IT manager to oversee security alongside daily operations.
Without clear platform-wide ownership, important decisions may be delayed or overlooked.
What leadership should ask: Who is accountable for identifying, prioritizing, and reporting cybersecurity risks across the platform?
If the answer differs by business unit, leadership may need to establish stronger governance.
5. Security Integration That Moves Too Quickly or Too Slowly
Connecting acquired businesses creates important security decisions.
Moving too quickly can introduce vulnerabilities if networks, applications, and user access are connected before risks are understood.
Moving too slowly can leave the organization operating with inconsistent security practices and limited oversight.
Neither extreme is ideal.
What leadership should ask: Are cybersecurity requirements built into our acquisition integration process, or are they addressed after operational integration is already underway?
A coordinated approach helps leadership balance integration objectives with appropriate risk management.