When mission requirements change faster than software can be delivered, the problem may not be your developers. It may be the system they’re working within.
For federal defense software organizations, delivering capability quickly is essential. But speed alone is not enough.
Every release must account for operational requirements, cybersecurity controls, system dependencies, testing, and mission continuity.
The challenge for technical leaders is improving delivery performance without compromising those responsibilities.
That requires looking beyond individual development teams and examining the complete software delivery process.
The Real Reasons Software Delivery Slows Down
When delivery timelines slip, organizations often respond by adding developers, increasing oversight, or introducing new tools.
Those actions may help in certain circumstances. But they rarely solve underlying problems when the delivery process itself creates delays.
Common constraints include:
Manual testing and validation. When regression testing depends heavily on manual effort, each change can require substantial time to verify.
Disconnected development environments. Inconsistent tooling, infrastructure configurations, and integration processes create additional engineering work.
Complex security and authorization requirements. Security reviews and approval processes can become difficult to coordinate when evidence collection is disconnected from development.
Legacy application dependencies. Tightly connected systems can make small changes difficult to isolate, test, and deploy.
Unclear ownership and priorities. When responsibilities are fragmented across contractors, program teams, and operational stakeholders, decisions take longer.
These issues are not necessarily failures of individual engineering teams. They are often symptoms of delivery models that have become increasingly difficult to manage.
DevSecOps Is More Than a Toolchain
DevSecOps is frequently associated with automated pipelines, security scanning, and continuous integration.
Those capabilities matter. But installing tools does not automatically create a more effective delivery organization.
Successful DevSecOps practices require alignment among engineering, security, operations, and program leadership.
The Department of Defense’s Software Modernization Strategy identifies software delivery, cloud capabilities, and process improvements as important priorities.
Its objectives include advancing DevSecOps, improving software deployment practices, and supporting continuous authorization approaches.
The strategic direction is clear: improving software delivery requires changes in technology, processes, and organizational responsibilities.
For technical leaders, the practical question is whether those elements are working together.
A modern pipeline cannot compensate for unresolved integration dependencies. Automated testing provides limited value if test environments do not reflect operational conditions. Security scanning alone does not eliminate the need for effective risk management and authorization.
Delivery improvement must address the entire system.
Five Areas That Deserve Closer Examination
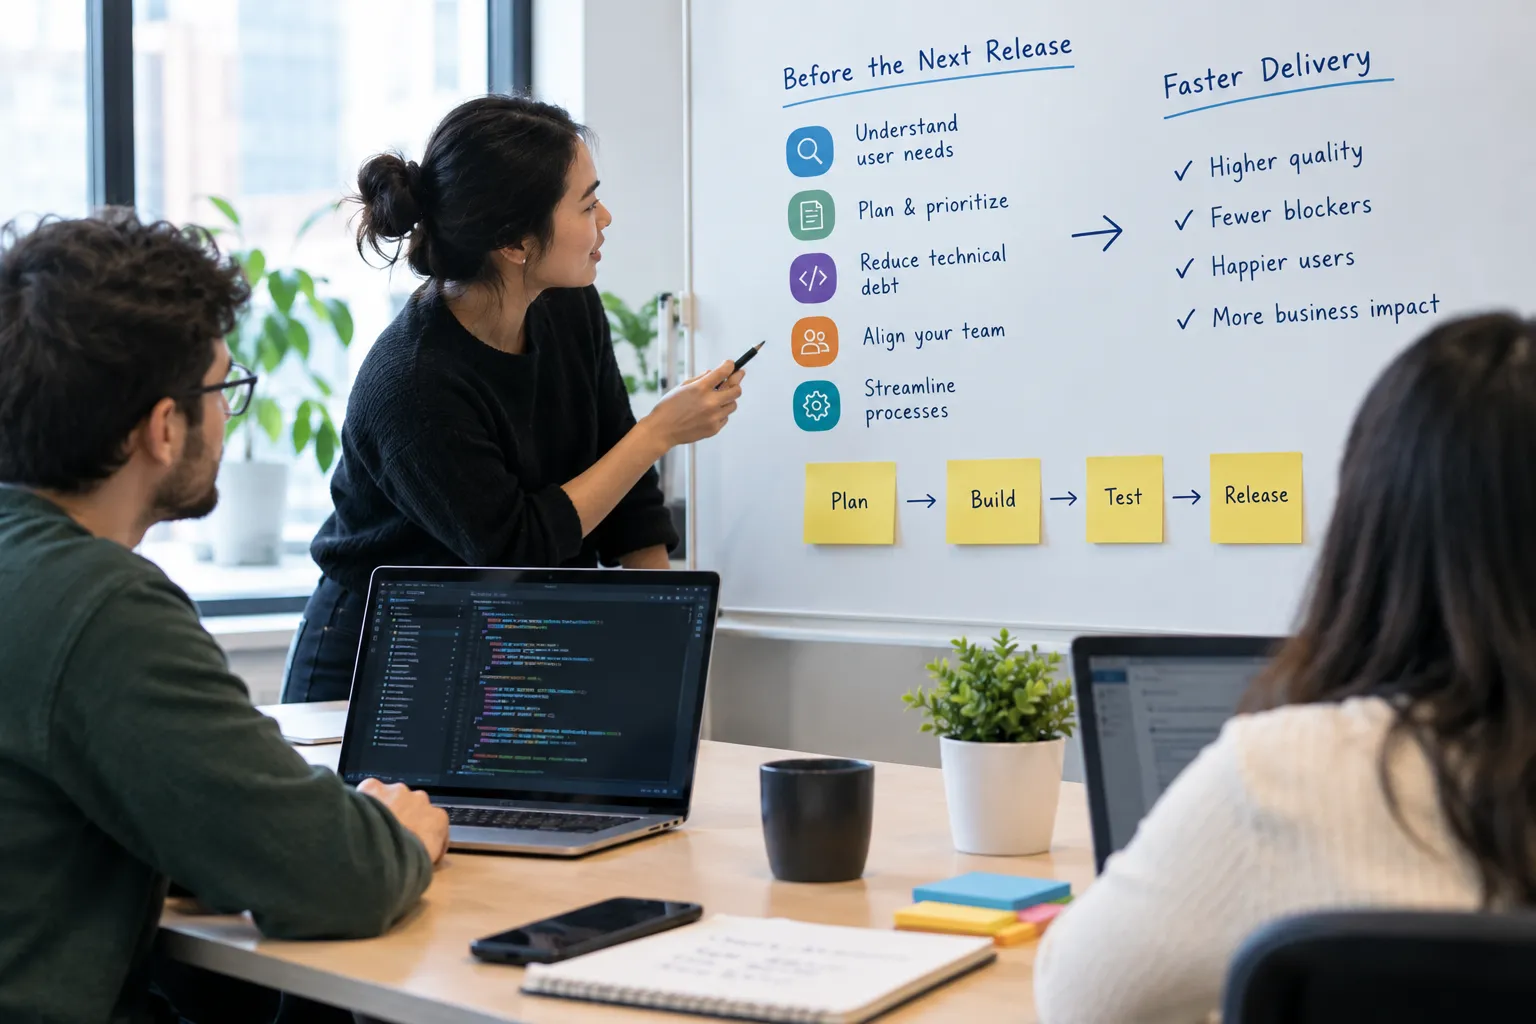
1. Identify Where Work Actually Slows Down
Before investing in additional engineering capacity, map the path from approved requirement to operational deployment.
Examine how much time is spent developing, waiting for reviews, resolving integration problems, testing, collecting security evidence, and preparing releases.
This helps distinguish productive engineering work from avoidable delays.
2. Strengthen Automated Testing
Automated testing can help teams detect defects earlier and reduce repetitive verification work.
The priority should be tests that meaningfully reduce risk, particularly around critical interfaces, security-sensitive functionality, and frequently modified components.
Automation must be designed around the application’s architecture and operational requirements.
3. Integrate Security Into Development
Security should be considered throughout the software lifecycle rather than treated as a final checkpoint.
Practical improvements may include automated vulnerability scanning, dependency analysis, configuration validation, and more consistent evidence collection.
These practices can support security assessments, but they do not replace required authorization decisions or guarantee an Authority to Operate.
4. Reduce Environment and Integration Friction
Inconsistent environments can introduce defects that are difficult to reproduce and resolve.
Standardized configurations, controlled infrastructure changes, and documented integration dependencies can improve engineering predictability.
The appropriate implementation must reflect the program’s security boundaries and approved operating environment.
5. Measure Delivery Outcomes, Not Activity
The number of completed tasks or lines of code written does not establish whether a program is delivering value.
More meaningful measures include:
- Lead time from approved change to deployment
- Deployment frequency where operationally appropriate
- Change failure rates
- Time required to restore service
- Defect escape rates
- Time spent waiting on external dependencies
These measures should be interpreted in the context of mission requirements. A safety-critical system may appropriately use a different release cadence from a lower-risk business application.
Where AI-Assisted Engineering Fits
AI-assisted development tools may help engineers with activities such as code analysis, documentation, test generation, and selected development tasks.
However, their value depends on the environment in which they operate.
For defense programs, leaders must evaluate data handling, approved tool usage, model access, code protection, software assurance, and human review requirements.
AI-generated code still requires appropriate testing, security validation, and engineering accountability.
The right question is not whether AI can generate code faster.
It is whether approved AI-assisted practices can improve measurable delivery outcomes without introducing unacceptable security, quality, or operational risk.
A controlled pilot with defined success measures is more useful than a broad promise of acceleration.
Build a Delivery Model That Supports the Mission
In its December 2025 report on weapon-system testing modernization, GAO identified opportunities to strengthen iterative testing, early tester involvement, and feedback practices in defense development.
These findings reinforce the importance of addressing delivery constraints early rather than relying on late-stage testing and correction.
For software engineering leaders, improving performance begins with understanding the current delivery model and identifying the changes that will produce meaningful operational benefits.
STG Consulting helps organizations connect technology decisions to performance, cost, and risk.
Our approach considers application architecture, engineering practices, security requirements, and organizational priorities to help leaders identify practical improvements and establish an execution plan.
Because delivering software faster matters only when the software is secure, reliable, and ready to support the mission.
Your mission can’t wait. Neither should your software.